

Dec 19, 2025 Newest SC-300 Exam Dumps – Achieve Success in Actual SC-300 Exam
Updated Microsoft SC-300 Dumps – Check Free SC-300 Exam Dumps (2025)
NEW QUESTION # 78
You have a Microsoft Entra tenant.
You open the risk detections report.
Which risk detection type is classified as a user risk?
- A. anonymous IP address
- B. unfamiliar sign-in properties
- C. Microsoft Entra threat intelligence
- D. password spray
Answer: C
NEW QUESTION # 79
Your company has an Azure AD tenant that contains the users shown in the following table.
You have the app registrations shown in the following table.
A company policy prevents changes to user permissions.
Which user can create appointments in the calendar of each user at the company?
- A. User4
- B. User1
- C. User3
- D. User2
Answer: D
NEW QUESTION # 80
You have a Microsoft 365 tenant and an Active Directory domain named adatum.com.
You deploy Azure AD Connect by using the Express Settings.
You need to configure self-service password reset (SSPR) to meet the following requirements:
When users reset their password, they must be prompted to respond to a mobile app notification or answer three predefined security questions.
Passwords must be synced between the tenant and the domain regardless of where the password was reset.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-sspr-deployment
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-authentication-security-questions
NEW QUESTION # 81
You have an Azure subscription that contains the resources shown in the following table.
You create a Microsoft Entra user named User1.
Which identities can you add to VM1 and App1? To answer, select the appropriate options in the answer area.
NOTE: Each correct answer is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 82
Drag and Drop Question
You have an Azure subscription that is linked to an Azure AD tenant named contoso.com. The subscription contains a group named Group1 and a virtual machine named VM1.
You need to meet the following requirements:
- Enable a system-assigned managed identity for VM1.
- Add VM1 to Group1.
How should you complete the PowerShell script? To answer, drag the appropriate cmdlets to the correct targets. Each cmdlet may be used once, more than once or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 83
You have a Microsoft 365 E5 subscription that contains three users named User1, User2, and User3.
You need to configure the users as shown in the following table.
Which portal should you use to configure each user? To answer, drag the appropriate portals to the correct users. Each portal may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated
NEW QUESTION # 84
You have Microsoft Entra tenant.
You need to configure the following External Identities features:
* B2B collaboration
* Monthly active users (MAU)-based pricing
Which two settings should you configure? To answer, select the settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 85
You have an on-premises Microsoft Exchange organization that uses an SMTP address space of contoso.com.
You discover that users use their email address for self-service sign-up to Microsoft 365 services.
You need to gain global administrator privileges to the Azure Active Directory (Azure AD) tenant that contains the self-signed users.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Create a self-signed user account in the Azure AD tenant.
2 - Sign in to the Microsoft 365 admin center.
3 - Respond to the Became the admin message.
4 - Create a TXT record in the contoso.com DNS zone.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/enterprise-users/domains-admin-takeover
NEW QUESTION # 86
You have a Microsoft Entra tenant that contains two groups named Group! and Group2 and the users shown in the following table.
Group2 is a member of Group1.
You configure an access review that has the following settings:
* Name: Review 1
* Select what to review: Teams + Groups
* Review scope: Select Teams + groups
* Group: Group1
* Scope: Guest users only
* Select reviewers: Group owners(s)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 87
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains a user named User1.
User1 has the devices shown in the following table.
On November 5, 2020, you create and enforce terms of use in contoso.com that has the following settings:
Name: Terms1
Display name: Contoso terms of use
Require users to expand the terms of use: On
Require users to consent on every device: On
Expire consents: On
Expire starting on: December 10, 2020
Frequency: Monthly
On November 15, 2020, User1 accepts Terms1 on Device3.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 88
You have a Microsoft 365 tenant named contoso.com.
Guest user access is enabled.
Users are invited to collaborate with contoso.com as shown in the following table.
From the External collaboration settings in the Azure Active Directory admin center, you configure the Collaboration restrictions settings as shown in the following exhibit.
From a Microsoft SharePoint Online site, a user invites [email protected] to the site.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 89
You have a Microsoft 365 tenant.
You need to Identity users who have leaked credentials. The solution must meet the following requirements:
* Identity sign-ms by users who are suspected of having leaked credentials.
* Flag the sign-ins as a high-risk event.
* Immediately enforce a control to mitigate the risk, while still allowing the user to access applications.
What should you use? To answer, select the appropriate options m the answer area.
Answer:
Explanation:
NEW QUESTION # 90
Your network contains an on premises Active Directory domain named conIoso.com. The domain contains the objects shown in the following table.
You install Microsoft Entra Connect. You configure the Domain and OU filtering settings as shown in the Domain and OU filtering exhibit. (Click the domain and OU Filtering tab.) You configure the Filter user and devices settings as shown in the Filter Users and Devices exhibit. (Click the filter Users and Devices tab).
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
Answer:
Explanation:
NEW QUESTION # 91
You have an Azure Active Directory (Azure AD) tenant that has multi-factor authentication (MFA) enabled.
The account lockout settings are configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
App code
60
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-mfa-mfasettings#account-lockout
NEW QUESTION # 92
You have a Microsoft 365 tenant and an Active Directory domain named adatum.com.
You deploy Azure AD Connect by using the Express Settings.
You need to configure self-service password reset (SSPR) to meet the following requirements:
When users reset their password, they must be prompted to respond to a mobile app notification or answer three predefined security questions.
Passwords must be synced between the tenant and the domain regardless of where the password was reset.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-sspr-deployment
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-authentication-security-questions
NEW QUESTION # 93
You have an Azure AD tenant that contains a user named User1. User1 is assigned the User Administrator role.
You need to configure External collaboration settings for the tenant to meet the following requirements: |
*Guest users must be prevented from querying staff email addresses.
*Guest users must be able to access the tenant only if they are invited by User1.
Which three settings should you configure? To answer, select the appropriate settings in the answer area.
Answer:
Explanation:
Explanation:
Box1 = User access is restricted to properties and memberships of their own directory objects (most restrictive). This setting ensures that guest users are prevented from querying staff email addresses and can access the tenant only if they are invited by User1.
Box2 =Only users assigned to specific admin roles can invite guest users. This setting ensures that guest users can access the tenant only if they are invited by User1.
Box3 = This setting enables guest users to sign up for the tenant only if they are invited by User1.
NEW QUESTION # 94
You have an Azure subscription that contains the users shown in the following table.
You need to implement Azure AD Privileged Identity Management (PIM).
Which users can use PIM to activate their role permissions?
- A. Admin1, Admin2, and Admin3
- B. Admin2 and Admin3 only
- C. Admin1 and Admin2 only
- D. Admin3 only
- E. Admin2 only
- F. Admin1 only
Answer: D
Explanation:
You cannot manage the following classic subscription administrator roles in Privileged Identity Management:
- Account Administrator
- Service Administrator
- Co-Administrator
https://learn.microsoft.com/en-us/entra/id-governance/privileged-identity-management/pim-roles
NEW QUESTION # 95
You have a Microsoft 365 tenant.
You configure a conditional access policy as shown in the Conditional Access policy exhibit. (Click the Conditional Access policy tab.)
You view the User administrator role settings as shown in the Role setting details exhibit. (Click the Role setting details tab.)
You view the User administrator role assignments as shown in the Rote assignments exhibit. (Click the Role assignments lab.)
For each of the following statement, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.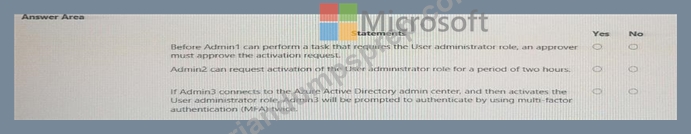
Answer:
Explanation:
NEW QUESTION # 96
You have a Microsoft 365 E5 subscription that contains two groups named Group1 and Group2 and the users shown in the following table.
The subscription contains a Conditional Access policy that has the following settings:
* Name: Policy1
Target resources
* Include
* All cloud apps
* Access controls
* Grant
* Requite multifactor authentication
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Yes, No, Yes
NEW QUESTION # 97
You have an Azure Active Directory (Azure AD) tenant.
For the tenant. Users can register applications Is set to No.
A user named Admin1 must deploy a new cloud app named App1.
You need to ensure that Admin1 can register App1 in Azure AD. The solution must use the principle of least privilege.
Which role should you assign to Admin1?
- A. Cloud application administrator in Azure AD
- B. Managed Application Contributor for Subscription1
- C. Application developer in Azure AD
- D. App Configuration Data Owner for Subscription1
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/roles/delegate-app-roles
NEW QUESTION # 98
Hotspot Question
You have an Azure Active Directory (Azure AD) tenant that has an Azure Active Directory Premium Plan 2 license. The tenant contains the users shown in the following table.
You have the Device Settings shown in the following exhibit.
User1 has the devices shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: No
Maximum number of devices: This setting enables you to select the maximum number of Azure AD joined or Azure AD registered devices that a user can have in Azure AD.
Box 2: Yes
You must be assigned one of the following roles to view or manage device settings in the Azure portal:
* Global Administrator
* Cloud Device Administrator
* Global Reader
* Directory Reader
Box 3: No
Additional local administrators on Azure AD joined devices (Device is Registered not Joined) Reference:
https://docs.microsoft.com/en-us/azure/active-directory/devices/device-management-azure-portal
NEW QUESTION # 99
You have an Azure Active Directory (Azure AD) tenant that has multi-factor authentication (MFA) enabled.
The account lockout settings are configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 100
......
Earning the Microsoft SC-300 certification can be a valuable addition to a professional's resume, as it demonstrates a high level of expertise in identity and access management in Microsoft Azure. Certification holders can take on key roles such as Identity and Access Administrator, Security Administrator, or Cloud Security Engineer. Additionally, the certification serves as a prerequisite for the Microsoft Certified: Security, Compliance, and Identity Fundamentals certification, which covers a broader range of security and compliance concepts in Microsoft Azure.
Actual SC-300 Exam Recently Updated Questions with Free Demo: https://exams4sure.briandumpsprep.com/SC-300-prep-exam-braindumps.html
